Shadow AI - Shine a light on it!
Aug 14, 2026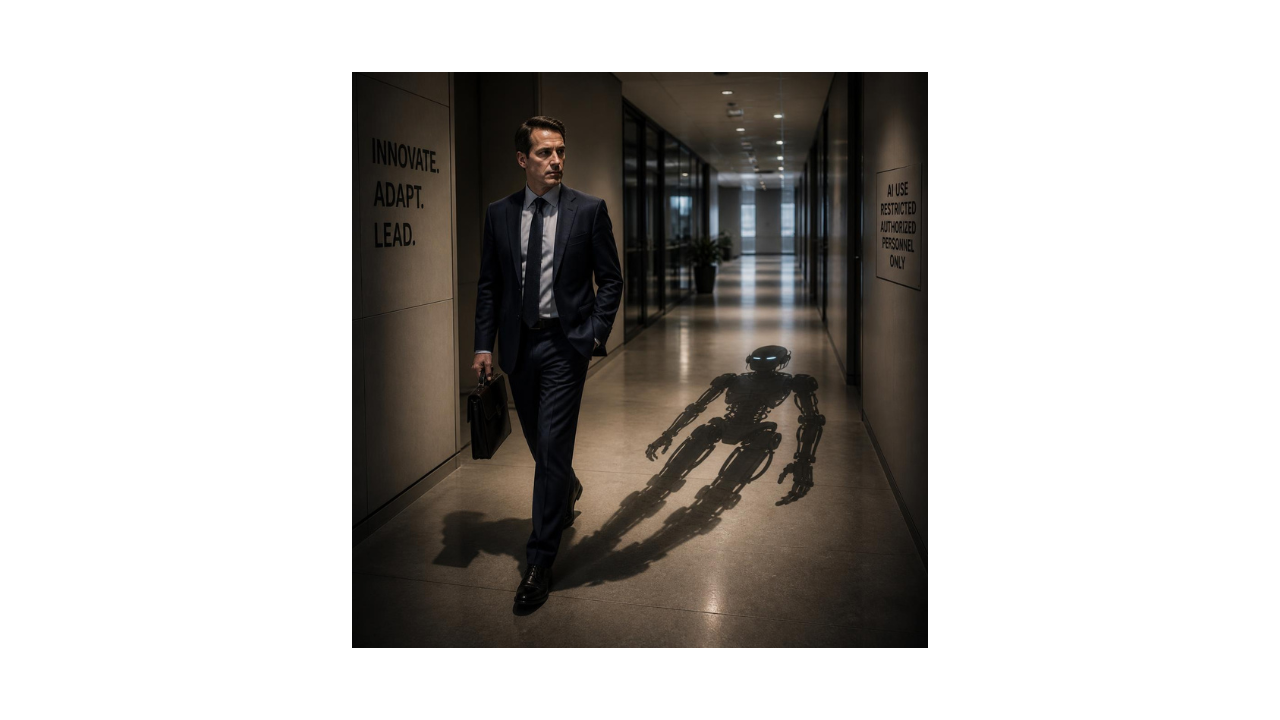
Shadow AI: The Risk Already Sitting Inside Your Organization
Someone in your organization used AI today.
Actually, let's make that a little more realistic.
Lots of people in your organization probably used AI today.
Someone asked it to improve an email. Someone summarized a document. Someone used it to analyze a spreadsheet, write a job description, create meeting notes, research a vendor, draft a report, fix a formula or turn three pages of corporate speak into something another human being might actually want to read.
And somewhere, someone may have copied information into an AI tool that they probably shouldn't have.
Welcome to Shadow AI.
It sounds ominous, doesn't it? Like something wearing a black cape lurking behind the server room.
The reality is considerably less dramatic.
And potentially much more important.
What Is Shadow AI?
Shadow AI is the use of artificial intelligence tools within an organization without formal approval, oversight or sometimes even the organization's knowledge.
It might be an employee using a free generative AI account to help write a report.
It could be a department subscribing to an AI application without going through IT.
It could be someone uploading a spreadsheet to an AI tool because they need help analyzing the data.
Most of the time, nobody is sitting at their desk thinking:
“Today seems like a lovely day to violate our AI governance policy.”
They're trying to get their work done.
That's what makes Shadow AI interesting.
The people creating the risk may be doing it for exactly the reason organizations encourage people to use technology in the first place:
To work faster. Work smarter. Solve a problem.
The intention may be perfectly reasonable.
The risk is still there.
You Can't Govern What You Don't Know Exists
Imagine your organization has spent months developing its approach to AI.
Policies have been written.
Approved tools have been selected.
Cybersecurity has weighed in. Legal has weighed in. Compliance has weighed in. Risk has weighed in.
Perhaps there is even an AI governance committee.
Lovely.
Meanwhile, Bob in Accounting found an AI tool Tuesday night that creates fantastic financial summaries.
Nobody knows Bob is using it.
Including, quite possibly, Bob's manager.
That's the Shadow AI problem in a nutshell.
Organizations can build impressive governance structures around the AI they know about while remaining completely unaware of the AI being used outside those structures.
And before we blame Bob, we should probably ask another question.
Why did Bob feel he needed to find his own solution?
Now the conversation gets more interesting.
Shadow AI Is Often Trying to Tell Us Something
Unauthorized technology use isn't always simply an employee problem.
Sometimes it's feedback.
Perhaps the approved technology isn't meeting people's needs.
Perhaps employees don't know which AI tools are approved.
Perhaps the approval process takes six months while the business problem needs solving by Friday.
Perhaps the AI policy is 47 pages long, lives somewhere on the intranet and hasn't been read since Legal proudly announced its publication.
Or perhaps the organization told employees:
“Use AI! Innovate! Be more efficient!”
and followed it immediately with:
“But don't use it until we've figured out what you're allowed to do.”
Mixed messages create interesting behavior.
If people see genuine value in AI and the organization doesn't provide a practical route for using it, some will find their own route.
That doesn't make unauthorized AI acceptable.
But understanding why people are using it gives us a much better chance of managing the risk.
The Problem Isn't AI. It's the Information We Give It.
Suppose I ask an AI tool:
“Give me five ideas for making a project meeting more productive.”
Not terribly frightening.
Now suppose I upload a confidential project report containing employee names, financial information, contract details, vendor pricing and information about a project that hasn't been publicly announced.
Same technology.
Very different conversation.
When people use AI tools without understanding how information is collected, processed, retained or potentially used by those systems, organizational data can travel somewhere it was never intended to go.
That might include:
- Confidential business information
- Personal or employee data
- Customer information
- Intellectual property
- Contractual information
- Financial data
- Investigation material
- Proprietary methodologies
And here is where training becomes important.
Telling employees “Don't put confidential information into AI” sounds perfectly reasonable.
Until we ask:
Does everyone know what the organization considers confidential?
We can't expect people to protect information if we haven't helped them recognize it.
Then There Is the Small Matter of Whether AI Is Right
Generative AI can produce something wonderfully polished.
It can also produce something wonderfully polished that is completely wrong.
That's a dangerous combination.
A poorly written wrong answer often makes us suspicious.
A confident, beautifully written wrong answer can stroll straight into a report wearing a suit and tie.
That means employees need to understand that AI output isn't automatically evidence.
It isn't automatically fact.
And it certainly isn't automatically correct because it sounds confident.
If AI helps draft an analysis, recommendation, report or decision, someone still needs to ask:
Where did this come from?
Can I verify it?
Does it make sense?
Would I be comfortable putting my name on it?
That last question remains one of my favorites.
“Fine. Let's Just Ban It.”
Tempting.
Also probably unrealistic.
Blanket bans can sometimes push AI use further into the shadows rather than eliminate it.
If employees believe a tool genuinely helps them do their jobs, some may continue using it quietly.
Now the organization has managed to achieve something rather impressive:
The risk still exists, but visibility has disappeared.
A stronger approach is usually to create clear boundaries.
What tools are approved?
What information can and cannot be entered?
Which uses require human review?
Which uses are prohibited?
When does Legal, Compliance, Cybersecurity, Privacy, Internal Audit or another specialist need to become involved?
And perhaps most importantly:
Where can employees ask questions before they make a mistake?
Good governance should help people make better decisions.
It shouldn't require them to become AI lawyers.
Ask Your People
If you want to understand Shadow AI in your organization, don't begin with a 72-question assessment.
Start with a conversation.
Ask:
What AI tools are you using?
Then try very hard not to look horrified by the answer.
If the first response employees receive is punishment, embarrassment or a lecture, congratulations. You have just taught everyone else not to tell you.
We need honest answers.
What tools are people using?
What are they using them for?
What problems are they trying to solve?
What information are they entering?
What AI capability do they wish the organization provided?
Those conversations can reveal risk.
They can also reveal opportunity.
Someone may have discovered a genuinely valuable use case that the organization could evaluate, govern and potentially make available more broadly.
Shadow AI isn't only a risk-management issue.
It can also be an innovation signal.
Governance Should Put Up Guardrails, Not Brick Walls
I like guardrails.
A guardrail doesn't stop you from travelling down the road.
It helps stop you from accidentally driving off the side of it.
That's how I think good AI governance should work.
Organizations need enough structure to protect information, people, customers and the business without creating so much bureaucracy that employees spend more time navigating the governance process than doing their jobs.
That means policies people can understand.
Approved tools people can actually use.
Training based on real situations rather than definitions.
Clear accountability.
Human oversight where it matters.
And a way to identify when something has gone wrong, or might be about to.
So, Is Shadow AI Already in Your Organization?
Probably.
And that doesn't necessarily mean you have an employee problem.
It means you have a question to answer.
Actually, several.
Do we know how AI is being used?
Have we given people practical guidance?
Are our approved tools meeting real business needs?
Do employees understand what information they can and cannot share?
Can people raise questions without fearing they've just confessed to a crime?
And perhaps the biggest one:
Are we governing the AI people are actually using, or only the AI we think they're using?
Because AI adoption isn't waiting patiently for every organization to finish writing its governance framework.
People are experimenting.
They're learning.
They're finding shortcuts.
They're solving problems.
That's exciting.
It also means our approach to AI governance needs to catch up with the way people really work.
Shadow AI doesn't disappear because we don't see it.
Sometimes the smartest thing an organization can do is simply turn on the light.
Stay connected with news and updates!
Join our mailing list to receive the latest news and updates from our team.
Don't worry, your information will not be shared.
We hate SPAM. We will never sell your information, for any reason.